Illustrative editorial image generated with AI.
An agent that can research a company does not need permission to email it. An agent that can draft an email does not automatically need permission to add someone to a sequence. Treating all four activities as one “sales automation” permission makes a useful assistant harder to control and harder to investigate when something goes wrong.
Define the action before connecting the account
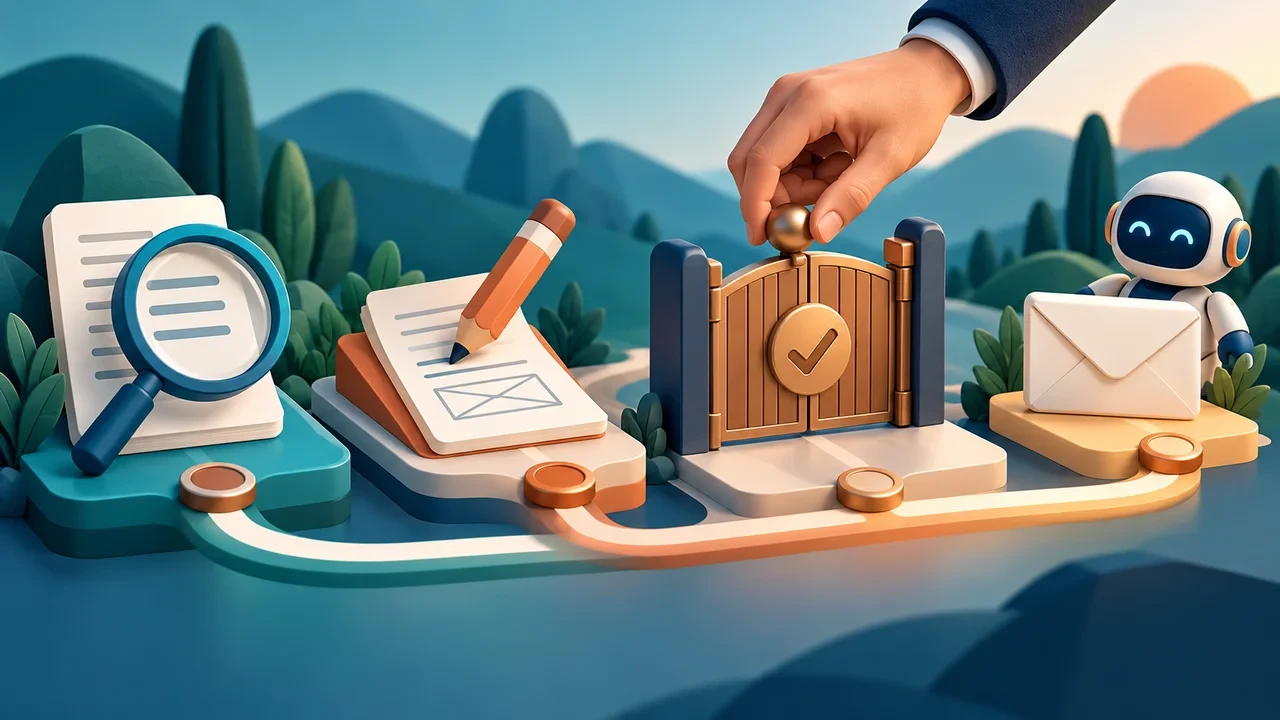
Start with four separate operations: research, draft, enroll and send. For each, specify the records it can read, fields it can change and downstream effects it can trigger. Enrollment is especially easy to underestimate: adding a contact to a live sequence can initiate future messages even if the current tool is not called “send.”
OWASP’s Excessive Agency guidance describes the risk of excessive functionality, permissions and autonomy. The matrix below is an editorial application of that principle to outbound sales, not a claim that a particular CRM implements these controls automatically.
A permission matrix for the first pilot
| Operation | Allowed scope | Required boundary |
|---|---|---|
| Research | Approved public sources and selected account records | No automatic overwrite of verified CRM facts |
| Draft | Create a proposed message linked to one contact | No mailbox send permission |
| Enroll | Approved contact and named sequence | Eligibility and suppression checks before entry |
| Send | Approved recipient, sender and message version | Recheck eligibility immediately before dispatch |
A pilot might enable only the first two rows. That is still useful if it saves research time and improves draft quality. Expand permissions only when the next action has a clear owner and measurable acceptance criteria.
Make approval refer to a concrete object
“Approved for outreach” is too vague for an audit. Capture the recipient identifier, address, sender mailbox, message revision, sequence version and expiration time of the approval. If the agent changes the recipient or materially rewrites the message afterward, require a new decision under your policy.
For example, a manager may approve one introductory draft for one contact. That does not necessarily authorize five follow-ups, an additional mailbox or all contacts at the company. Show the reviewer what the requested action actually starts, including scheduled downstream actions.
Enforce restrictions outside the prompt
A written instruction to “never contact suppressed leads” is not enough if the sending tool accepts arbitrary recipients. The execution layer should evaluate the current suppression state, ownership rules and permitted campaign before it sends. Check at execution time because a recipient’s status can change after the draft was approved.
Credential choice matters too. Microsoft’s Copilot Studio security-scan documentation flags changes from end-user credentials to maker-provided credentials as a configuration risk to review. In any platform, inspect whose authority a connector uses; a narrow-looking action can still run through a broadly privileged account.
Test the boundaries with ordinary failure cases
- A contact is suppressed between approval and the scheduled send.
- The draft has a new revision but the old revision was approved.
- A timeout occurs after dispatch and the agent retries.
- A contact appears twice under different CRM records.
- A research page contains instructions telling the agent to change its workflow.
The expected outcomes should be explicit: block, request review, reuse the existing send result or discard instructions from external content. Use test recipients and a non-production sequence to establish these behaviors before granting live sending access.
Measure control as well as output
Keep a compact event record of proposed action, policy result, reviewer, executed action and external result identifier. Store enough detail to explain an event without unnecessarily duplicating sensitive customer data. A team should be able to stop future sends promptly and identify the contacts already affected.
Track accepted drafts, reviewer changes, prevented duplicate sends and suppression blocks alongside replies or meetings. A high activity count with unclear authority is not a successful pilot. Our CRM agent audit-trail guide explains how to connect those records to operational review.